Platform · Identity Intelligence Graph
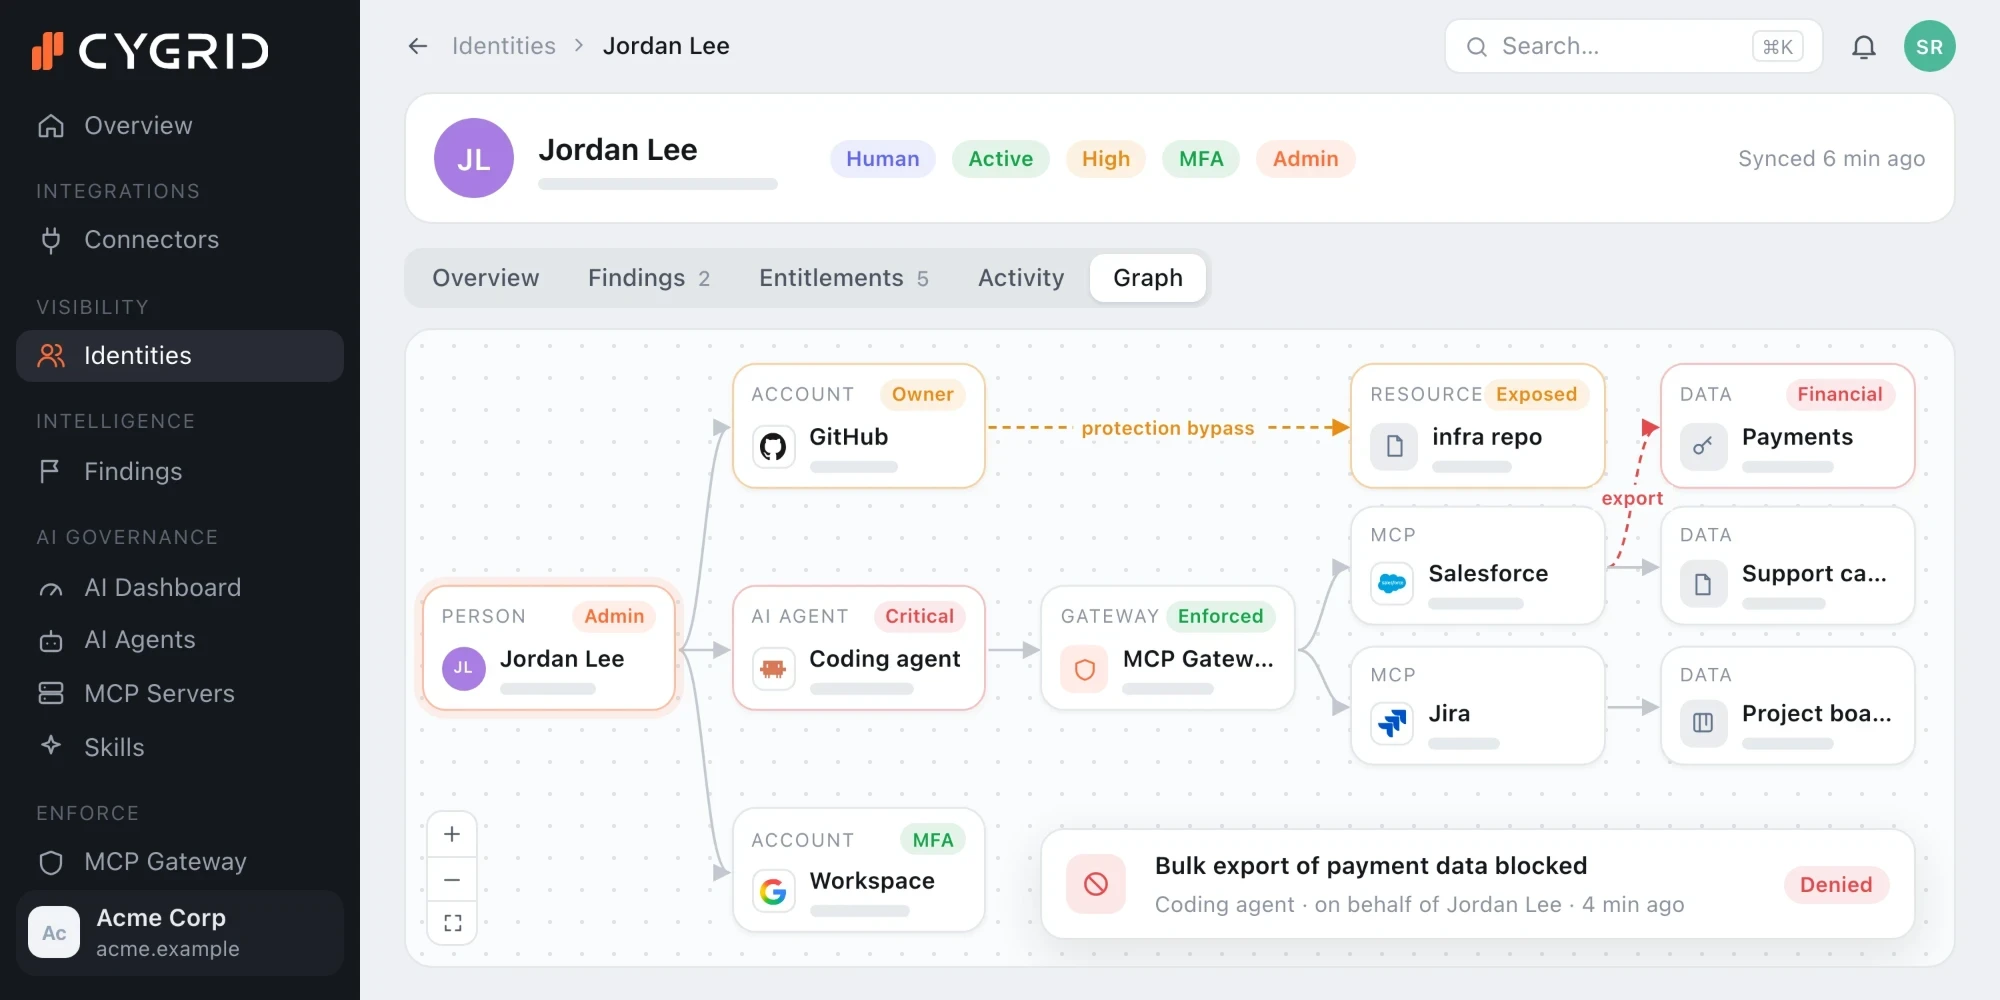
Visibility
1 · PEOPLE
Human
Employees, contractors, admins and partners, with their permissions, roles and risky privileges.
2 · MACHINES
Non-human
Service accounts, OAuth clients, API keys, CI/CD tokens and cloud workloads: the biggest blind spot and a leading source of breaches.
3 · AGENTS
AI agent
LLM agents, automation bots, workflow agents and MCP servers: a fast-growing identity class with no governance today.
Risk intelligence
Built for actions, not accounts
Identity providers model access. Governance tools model entitlements.
Cygrid models the action: the permission actually in play, in full context.
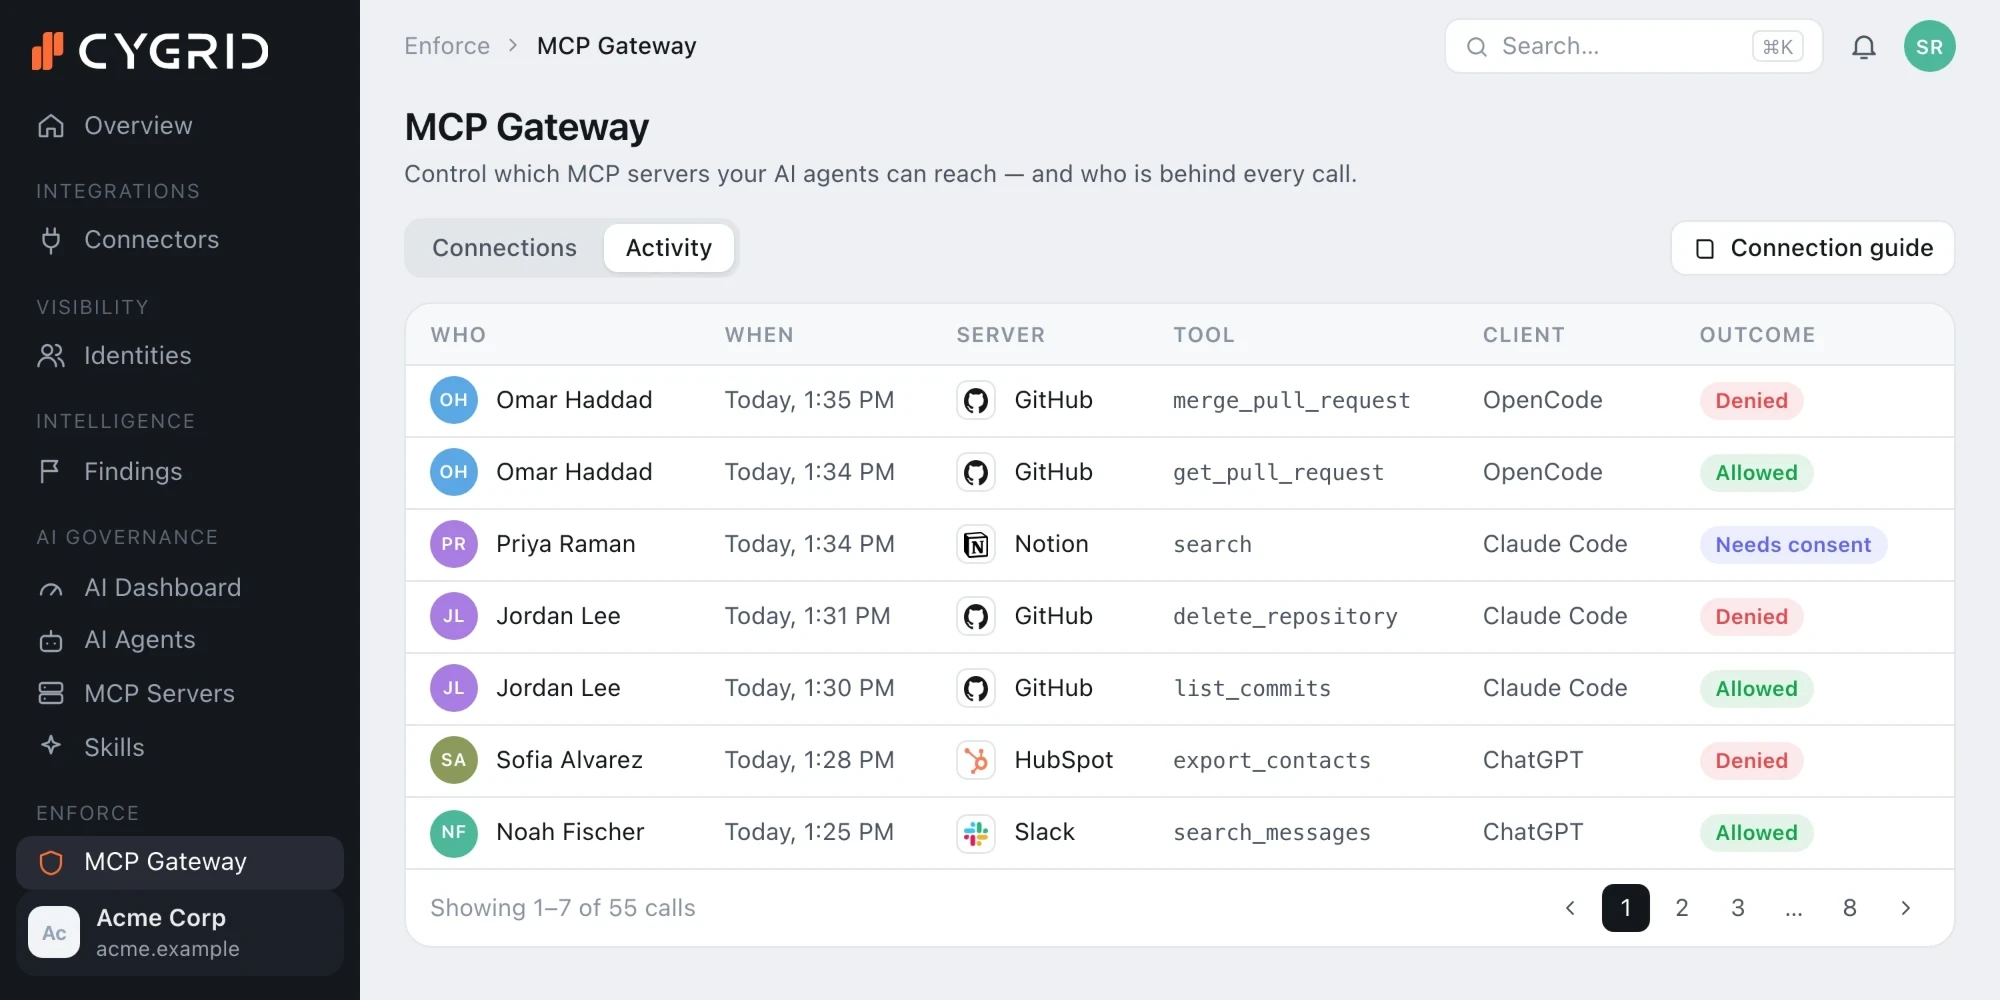
Access is modelled as SaaS actions rather than roles, so risk can be compared across tools.
Who
Human, non-human identity or AI agent, and who authorised it.
What
The permission actually in play, not the one on paper.
Where
Which SaaS, cloud account or MCP boundary.
Doing what
The action and its parameters, at the moment it happens.
Use cases
WHILE ACCESS EXISTS
Shadow AI agent appears in Google Workspace
A user connects an AI assistant to Gmail, Drive and Calendar without approval. Cygrid spots it and, once you approve, revokes its access.
WHILE ACCESS EXISTS
Orphaned org-admin API key in Atlassian
An admin key left behind by someone who has left still has full power. Cygrid finds it, with its creator and last use, and revokes it on your approval.
WHILE ACCESS EXISTS
Departed employee still an Atlassian admin
When someone is offboarded, Cygrid removes the Atlassian admin role they kept, with their content and seat intact.
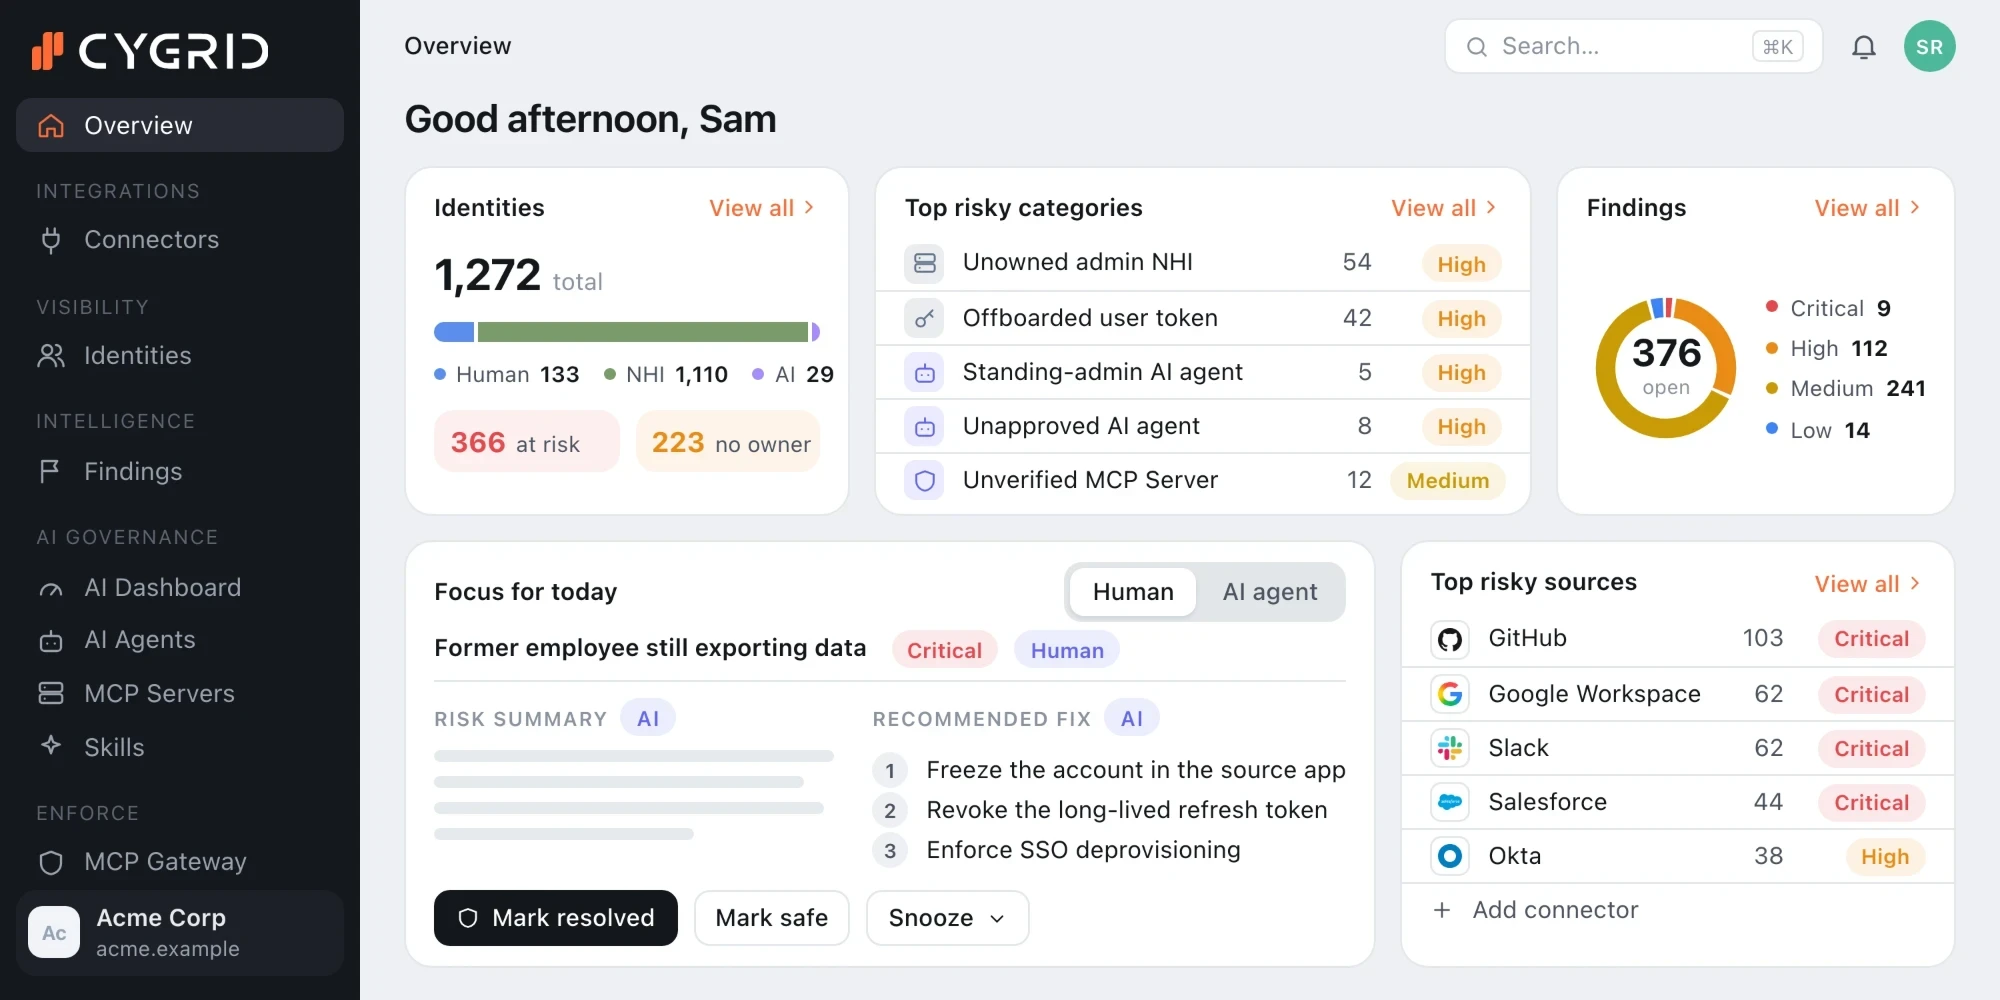
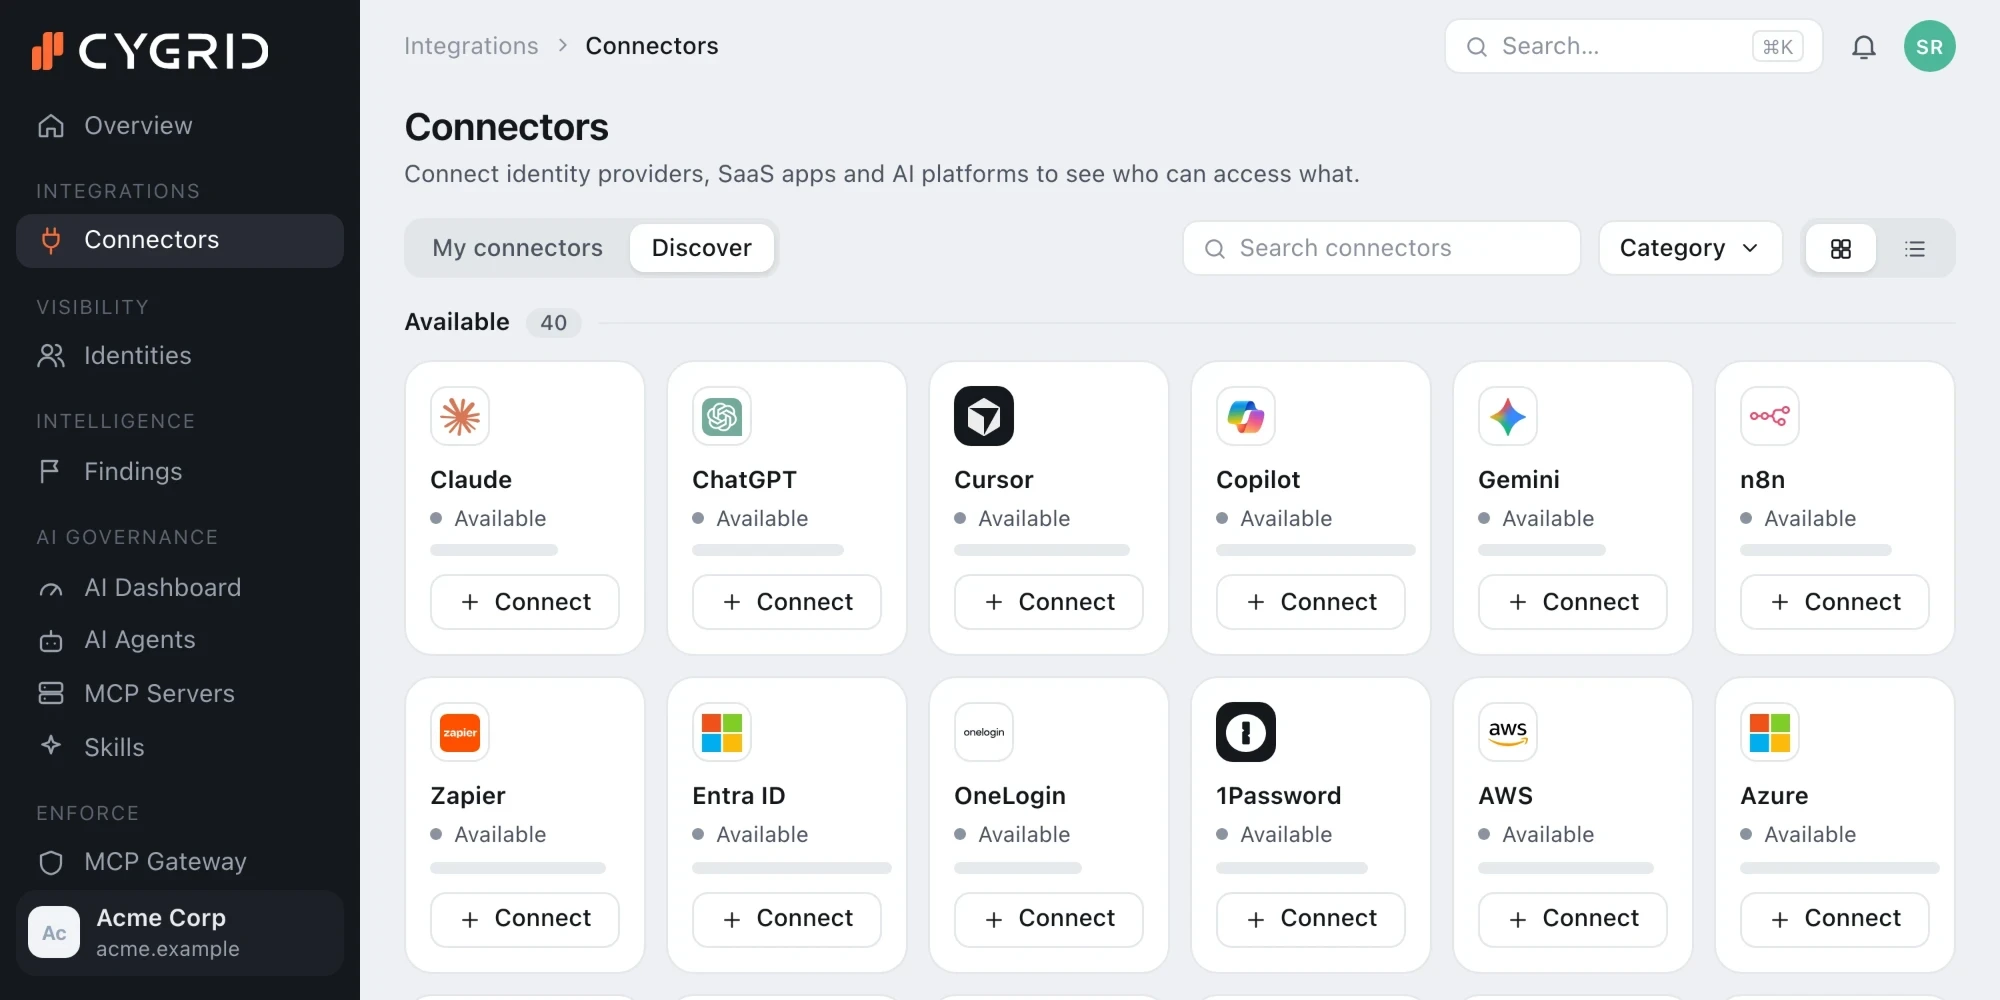
Every identity, what it can do, and your top risks ranked by business impact.